Yes
Module A: you self-declare
You draw up the technical documentation and sign the EU declaration of conformity yourself.
Radio Equipment Directive 2014/53/EU · mandatory since 1 Aug 2025
Technical documentation, test plan and EU declaration. AI drafts the file from your documents in about two to three weeks, testing not included; you review, sign and stay in control.
We reply within 24 hours to schedule a call, then a personalised demo and a proposal with pricing.
For each asset persistently stored on the equipment
DT.SSM-1.DN-1
Is the storage protected by physical or logical measures in the equipment’s target operational environment?
DT.SSM-1.DN-2
Is the storage implemented by a secure storage mechanism?


01What EN 18031 asks
Each part answers one essential requirement of the Directive.
Article 3(3)(d)
EN 18031-1
Internet-connected radio equipment must not harm the network or misuse its resources.
Article 3(3)(e)
EN 18031-2
Radio equipment that can process personal, traffic or location data: internet-connected equipment, and radio toys, childcare equipment and wearables even without an internet connection.
Article 3(3)(f)
EN 18031-3
Internet-connected radio equipment that lets the user transfer money, monetary value or virtual currency.
One line fits? Then RED Cybersecurity most likely applies: it is mandatory for the radio equipment named in Delegated Regulation (EU) 2022/30.
With a data connection, the CRA applies too: reporting since 11 September 2026, in full from 11 December 2027. See what the CRA requires
02Your route to conformity
Applying EN 18031 itself is voluntary, but it is the harmonised standard: applied in full, it gives a presumption of conformity and opens the self-declaration route.
Do you apply the relevant parts of EN 18031 in full, with none of the restrictions of Implementing Decision (EU) 2025/138?
Yes
You draw up the technical documentation and sign the EU declaration of conformity yourself.
No
You apply the standard only in part, or a restriction applies, for example a password the user does not have to set. Today this includes every product under Article 3(3)(f) (payments): a restriction on EN 18031-3 (clause 6.3.2.4) removes its presumption of conformity.
The technical file goes to a Notified Body, for EU-type examination (Modules B + C) or an assessment of your full quality assurance system (Module H). The same file RedComply prepares is what you hand over.
Before you sign, RedComply explains each restriction and why it matters, and records the route you take in the declaration. RedComply is a self-assessment tool, not a Notified Body: you review, sign and remain responsible.
03Time to a review-ready file
One file takes 6 to 12 months
and €10–20k per product.
The technical documentation: 87 tables under EN 18031-1 and -2, 74 of them requirement tables filled row by row.
The test plan: a conceptual assessment for each of its 46 requirements, and tests to plan for 43 of them.
The declaration: signed last, once no outcome in the documentation and no verdict in the test plan is a FAIL.
Manual figures: public estimates and consultant price lists, September 2026. Counts: RedComply’s templates for EN 18031-1 and -2.
About 2 to 3 weeks
of drafting, typically. Testing time comes on top and depends on your product.
No consultant hours for drafting.
Define the project
One product family and the parts of EN 18031 that apply to it.
Upload what you have
Datasheets, architecture and policies go into the project’s Knowledge Base, encrypted in transit and at rest.
AI prepares the drafts
The tables’ rows drafted from your Knowledge Base, with the document behind each fact; the decision trees then compute the outcome.
You review and sign: You stay in control
Edit and approve the documentation and the test plan; with your tests done, sign the declaration. You stay responsible as the manufacturer.
“We are forty people and nobody does compliance full time. Honestly, I expected another subscription we would abandon within a month. Instead the August deadline came and went and our documentation was already done.”

Giancarlo PeruzziCEO, Sarvento Automazione s.r.l.
04See it working
The RedComply dashboard on an EN 18031 project; waiting times are shortened. No sound; pause it at any time.
05What you get
Technical documentation
Every EN 18031 requirement has its own table, with the standard's decision tree built into the columns. The AI fills the rows from your documents; you check each outcome and the justification behind it.
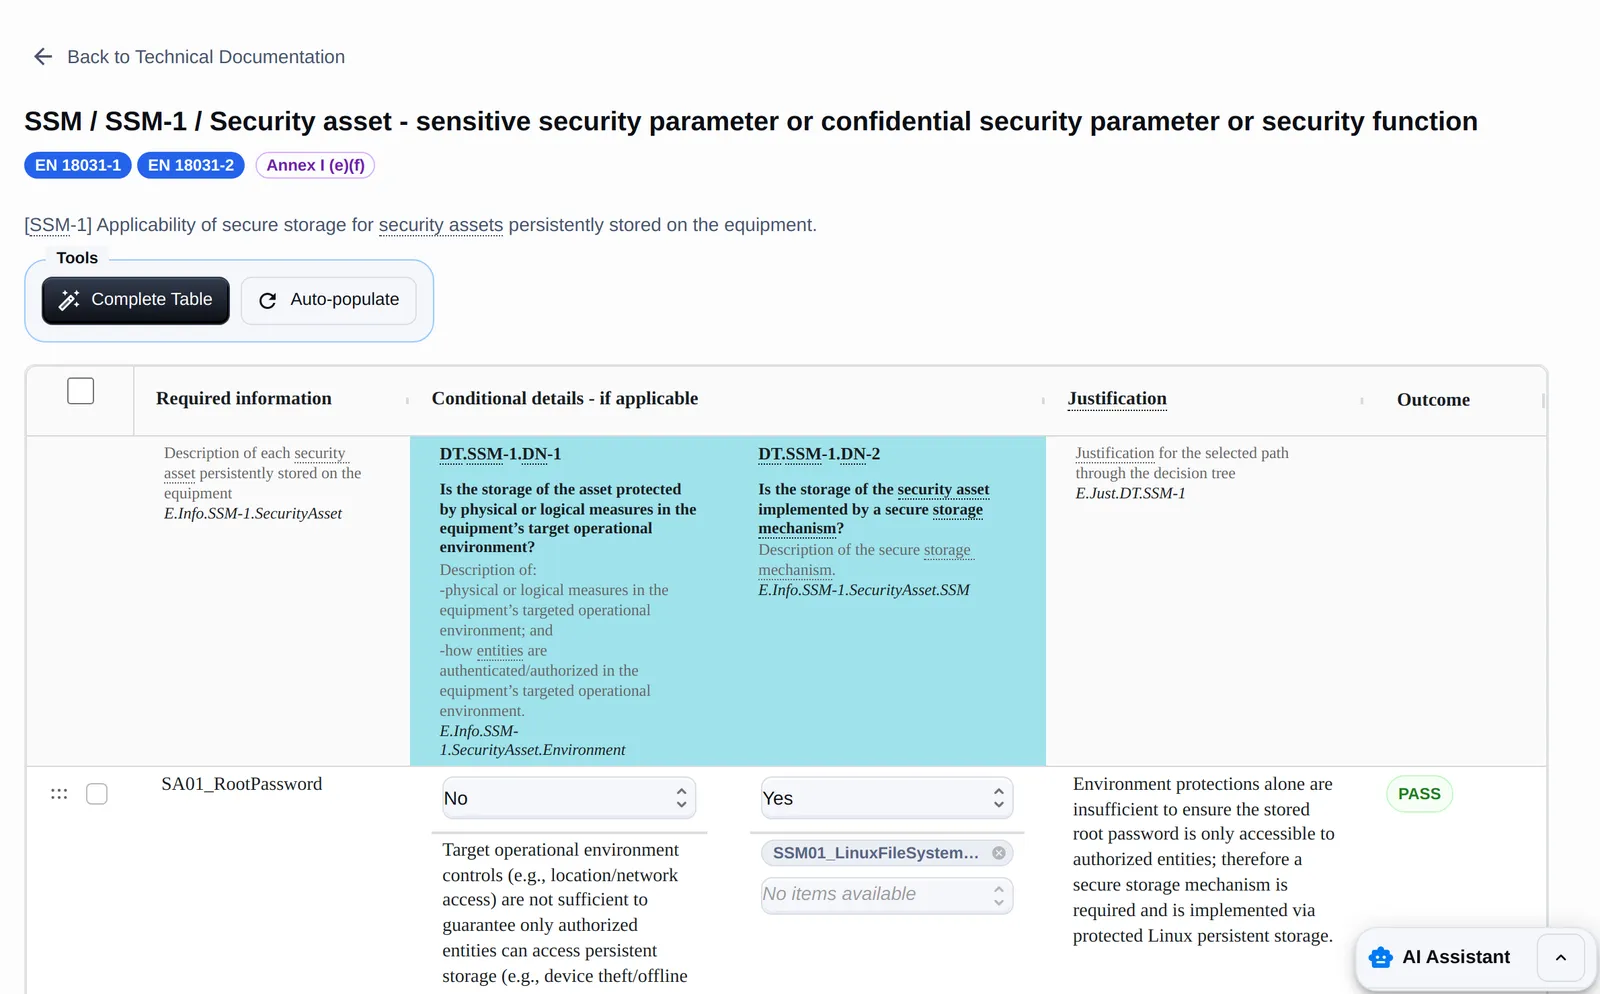
SSM-1 · Security asset table
AI assistant
The assistant works from your Knowledge Base: datasheets, architecture, policies and test reports. It completes tables, answers questions about the standard and points out gaps, and it asks before it saves.
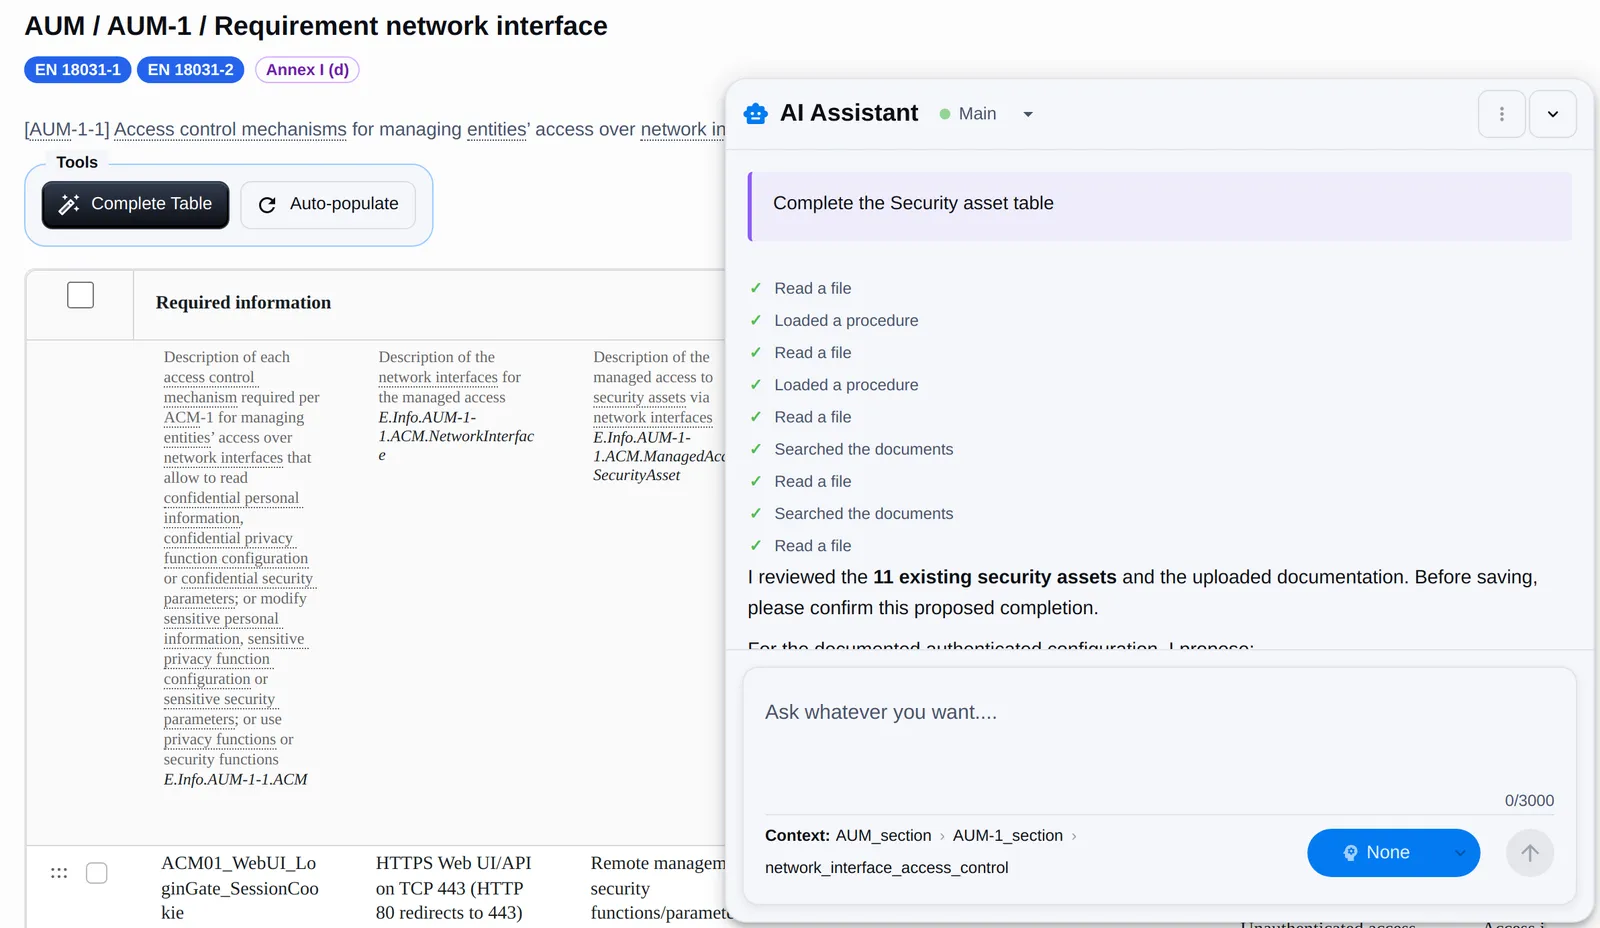
AI assistant · Knowledge Base
Complete the Security asset table
Before saving, please confirm this proposed completion.
Test plan
The test plan follows the standard's three assessment types: conceptual assessment of the documentation, functional completeness on the device, and functional sufficiency through real tests. RedComply structures the plan and records the evidence; the tests are run by you or a lab of your choice.
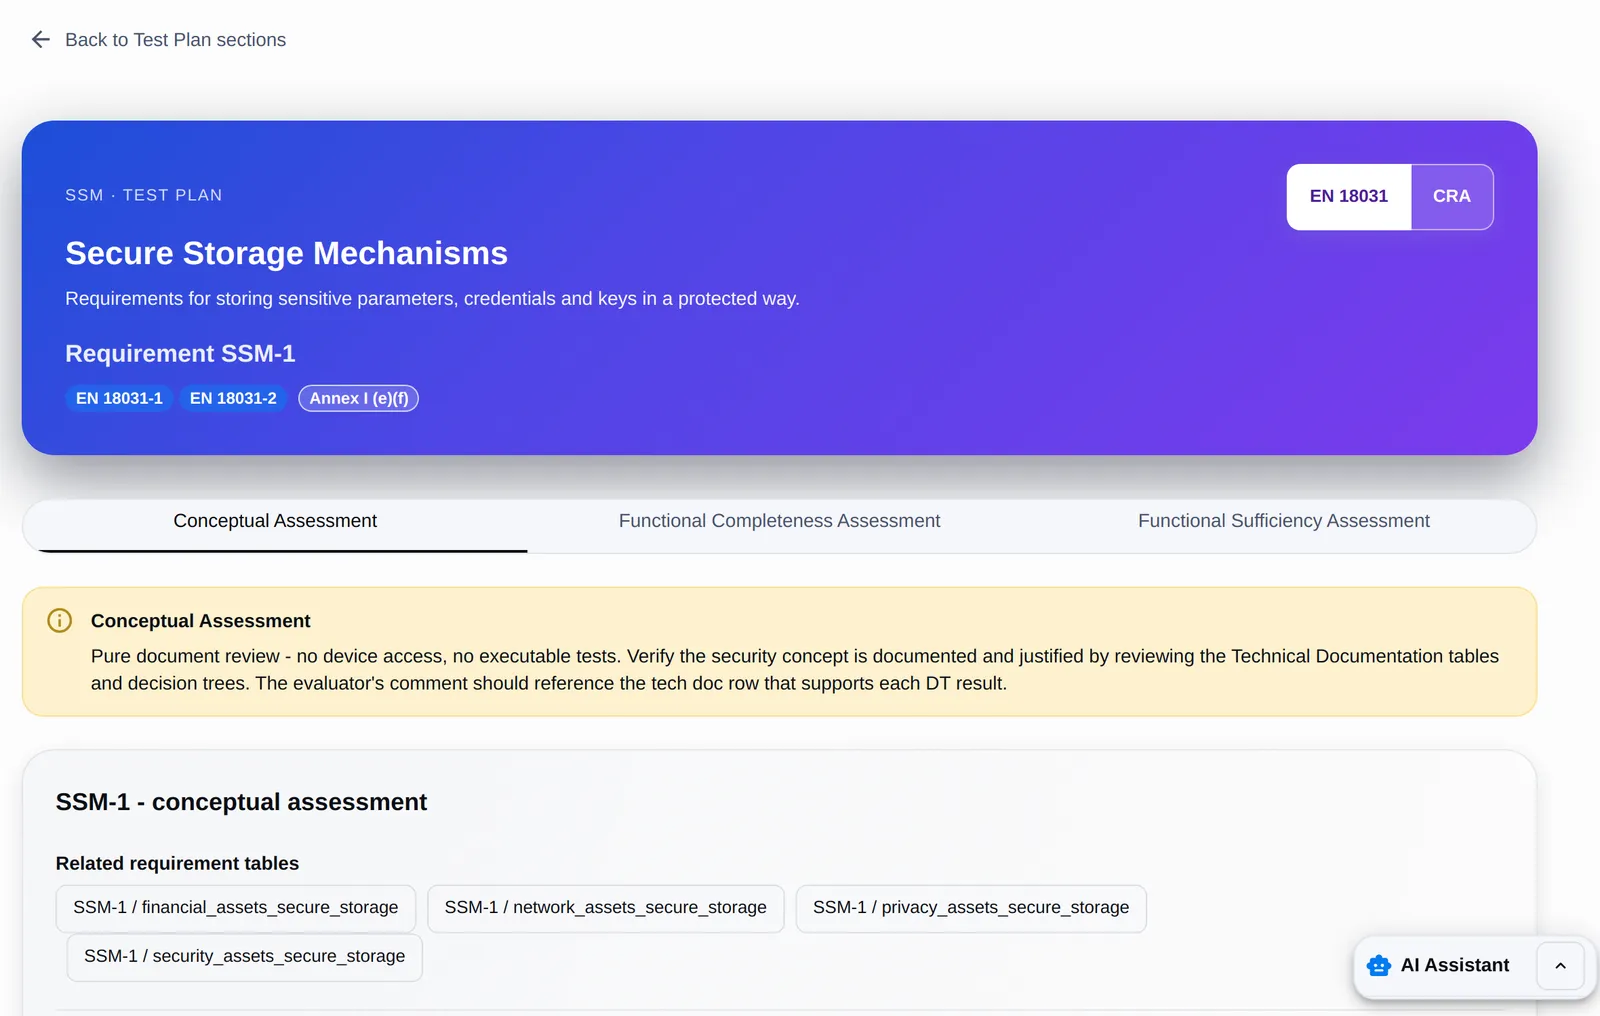
Test plan · three assessment types
Declaration
Review the declaration fields, sign, and generate your EU declaration of conformity, with EN 18031 listed for Article 3(3)(d), (e) and (f), together with the technical documentation and test plan PDFs and a single bundle. Every version is kept.
EU declaration of conformityPDF
06What manufacturers say
“I have been through notified body routes twice and did not want a third. RedComply kept us on the Module A self-declaration path: every clause mapped, every verdict traceable. Our reviewer found nothing to send back. For a smart-meter portfolio like ours, staying on the self-declaration path is worth real money.”

Silvia ContariniHead of Certification, Metrivolt s.r.l.
“I am the entire compliance department here, so the structure was the value: sections, decision trees and verdicts in one place instead of my folder of Word files. When our biggest customer asked for proof of EN 18031 conformity, I exported it the same afternoon. It survived first contact with a port authority's documentation request, which is the only benchmark that matters to me.”

Claire DuffieldCompliance Officer, Greyport Telemetry Ltd
“Half our devices are LoRa nodes sitting in fields, so the network assets section really mattered for us. The auto-populated asset inventories saved me from a spreadsheet I was dreading, and the test plan generation is the feature I did not know I needed. I did it all between firmware releases without pulling anyone off the roadmap, which honestly surprised me.”

Matteo ColasantiEmbedded Engineer, CampoSense s.r.l.
MCP · In pilot
Connect the coding agent your developers already use, such as Claude Code, Codex, Cursor or another agent that supports the Model Context Protocol (MCP). It answers RedComply's questions from the repository on your machine, with file references; RedComply drafts the technical documentation tables and you review them.
07Monitoring
Every night
Upload each product's SBOM. RedComply scans it every night against vulnerability databases and emails you when new or changed vulnerabilities appear.
After a product change
After a firmware or hardware change, update what is affected, re-check the verdicts and, when the change calls for it, issue a new version of the declaration.
CRA · Regulation (EU) 2024/2847
RedComply reuses your EN 18031 tables in the CRA technical documentation and adds the rest: EN 18031 covers part of the CRA’s Annex I.
The cybersecurity requirements of RED Article 3(3)(d), (e) and (f) are mandatory since 1 August 2025 for the radio equipment named in Delegated Regulation (EU) 2022/30. Applying EN 18031 itself is voluntary, but it is the harmonised standard: applied in full, it gives a presumption of conformity and opens the self-declaration route.
Your files stay in your project and are encrypted in transit and at rest. The platform is hosted in the European Economic Area; AI functions run through providers in the United States. We are working towards ISO 27001 certification.
Yes, under Module A, if you apply the relevant parts of EN 18031 in full and none of the restrictions in Commission Implementing Decision (EU) 2025/138 applies, such as a password the user does not have to set. Products under Article 3(3)(f) (payments) need a Notified Body today, because a restriction on EN 18031-3 (clause 6.3.2.4) removes its presumption of conformity. RedComply explains each restriction before you sign.
No. RedComply is a software platform for self-assessment, not a Notified Body. It prepares drafts and organises the evidence; you review, sign the declaration and remain responsible as the manufacturer. If you need a Notified Body, the same file is what you hand over.
No. RedComply builds the test plan from the standard's three assessment types and records the results and the evidence. Functional tests, such as network scans or penetration tests, are run by you or a test lab, and their reports go into your Knowledge Base.
Drafting a file with RedComply typically takes about two to three weeks, against six to twelve months by hand. Testing time comes on top and depends on your product.
RedComply shows which requirements a change affects. You update those parts, re-check the verdicts and, when the change calls for it, issue a new version of the declaration. The nightly SBOM scans keep checking the components of every release.
Templates are the starting point. The AI assistant reads your datasheets, architecture and policies and drafts the answers into the EN 18031 tables, with the source for each one; the decision trees then compute the outcome. You review and approve every answer.
Today · · RED cybersecurity mandatory since
Start with one product family and review your first drafts within days.
Request a demo and a pricing quote for your products.
We use cookies and similar tools to make this site work, to measure usage, and (with your permission) to record sessions for product research. You can change your choice any time via "Cookie preferences" in the footer. Read our cookie policy